


The threat landscape today
90%
of vulnerabilities are introduced during coding and build stages
33%
of all successful attacks target web applications
60%
of pentests entered through web applications
Source: PT SWARM penetration testing reports, H2 2024 — Q3 2025
A high-precision platform to secure your code. Find actionable risks without the noise
What is Application Inspector?
An AppSec tool that combines SAST, SCA, and DAST in one platform — plus ML-based malicious code detection and secrets detection. It scans your source code and open-source libraries, confirms what’s actually exploitable, and helps security and development teams focus on the same list of real, actionable risks.
Quality Gates
Automatic decision making
OWASP Top 10
Full compliance coverage
CI/CD systems
Integrated out of the box
Malicious code & secrets
Found with ML and data-flow analysis, not signatures

What Application Inspector does for your team
Produce a full software bill of materials, see which open-source components create real risk — and catch malicious code planted in packages: backdoors, hidden execution, data exfiltration. ML analysis, not signatures.
See every dependency — and what’s hiding in it

Fix real problems, not false alarms
Smart analysis eliminates unnecessary alerts so your team fixes real problems.
Find issues before you commit
Findings and fix guidance appear inside VS Code, Visual Studio, and JetBrains — including hardcoded passwords, API keys and tokens, caught before they ever reach the repository.

Prioritise by business risk
Set your own security rules and focus on what impacts your business — not generic severity scores.


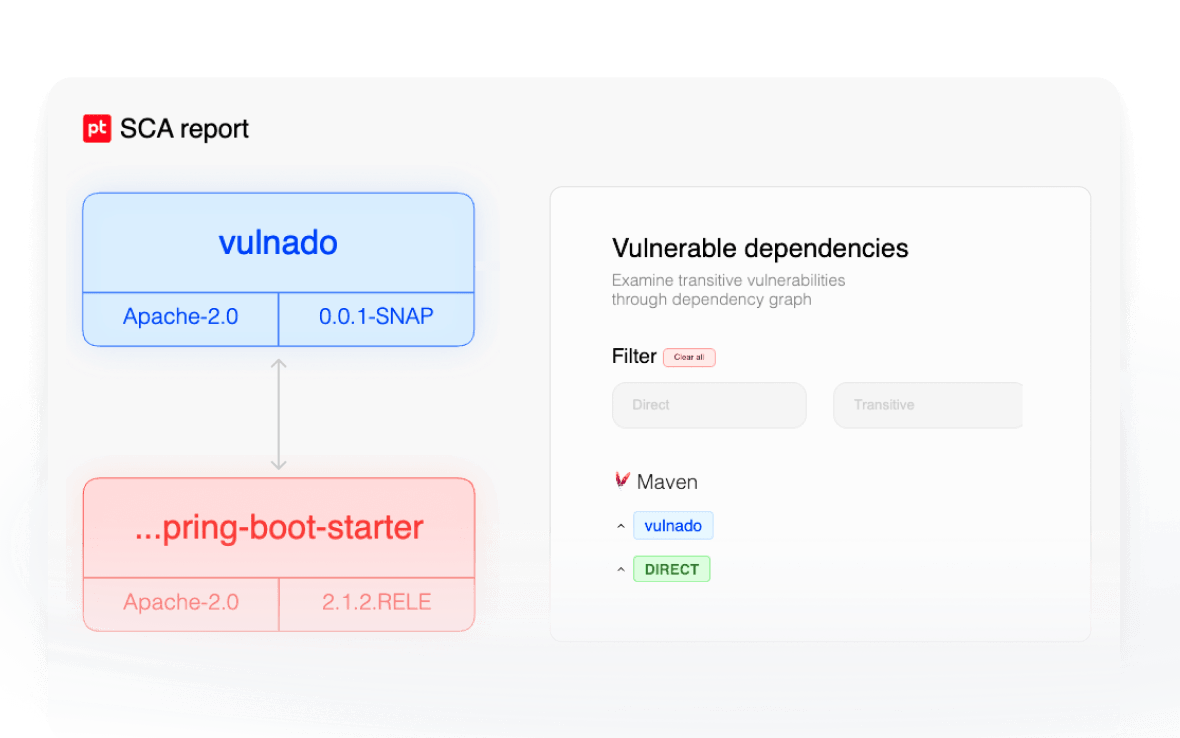
See every dependency — and what’s hiding in it
Produce a full software bill of materials, see which open-source components create real risk — and catch malicious code planted in packages: backdoors, hidden execution, data exfiltration. ML analysis, not signatures.
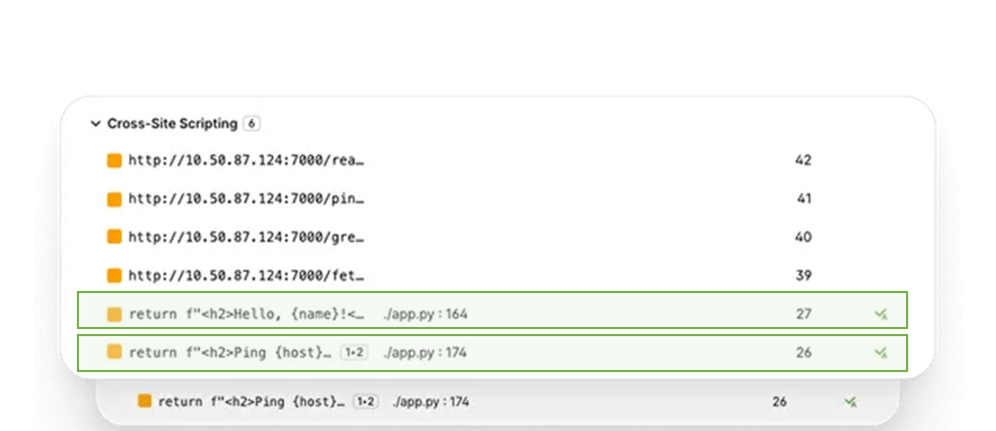
Fix real problems, not false alarms
Smart analysis eliminates unnecessary alerts so your team fixes real problems.
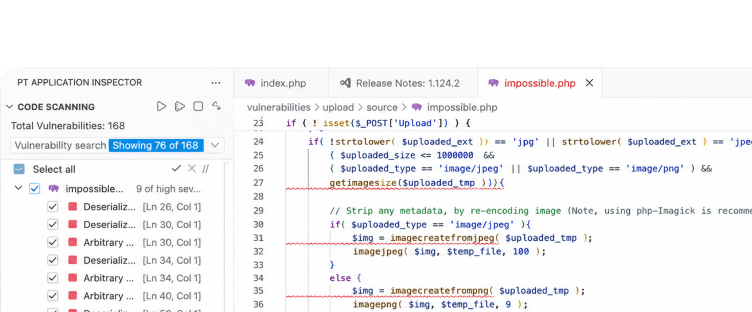
Find issues before you commit
Findings and fix guidance appear inside VS Code, Visual Studio, and JetBrains — including hardcoded passwords, API keys and tokens, caught before they ever reach the repository.
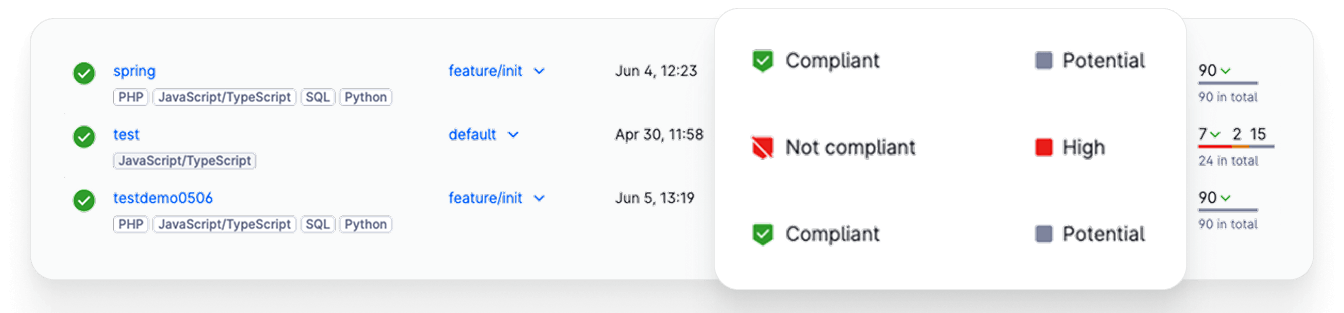
Prioritise by business risk
Set your own security rules and focus on what impacts your business — not generic severity scores.

Four ways to scan — pick what fits your workflow

Stand-alone scanning of files, folders, and archives
Application Inspector works as a self-contained analyzer — no integration needed. Upload a file, a project folder, or a ZIP archive through the interface and get a full security report in minutes. Perfect for one-off audits, third-party code reviews, or a quick check before a release.

Direct connection to your Git repositories
Connect Application Inspector to any Git repository over HTTPS or SSH. Scan specific branches, tags, or commits without manual uploads, and re-run analysis on every new revision. Works with GitHub, GitLab, Bitbucket, and self-hosted Git servers.

Built-in plugins for your CI/CD pipeline
Add security checks to every build. Out-of-the-box plugins for GitLab CI, GitHub Actions, Jenkins, and Azure DevOps run on each pipeline trigger, block builds with critical vulnerabilities, and post results back to your dashboards. Shift left — without changing how your team already works.

Scan code right inside your IDE
Catch vulnerabilities the moment they’re written. Native extensions for Visual Studio Code, Visual Studio, and JetBrains IDEs (IntelliJ IDEA, PyCharm, WebStorm, GoLand, and more) give developers inline findings, fix guidance, and one-click navigation to the affected line — without leaving the editor.
Get 2026 DevSecOps Strategy for free
Looking to accelerate releases without sacrificing security? We analyzed pipelines in e-comm, fintech and digital logistics and speeded up their time-to-market while reducing vulnerability risks by up to 60%
Leave your contacts to receive a strategy tailored to your business.
Leave your contacts to receive a strategy tailored to your business.
I give my consent to the processing of my personal data in accordance with the terms of the Privacy Notice.
Сообщение об успешной отправке!
How Application Inspector fits into your workflow
Connect your sources, run smart analysis, and get results right inside the tools your team already uses


What Application Inspector does
We don't just show you vulnerabilities.
We show you which ones really matter.
We show you which ones really matter.
All videos available with Indonesian subtitles
Scans your own code and open-source libraries for vulnerabilities (SAST/SCA)
Catch issues before they reach production. Find hidden risks in third-party components
Confirms real vulnerabilities — automatically (AutoCheck)
No manual verification. Only real, exploitable risks reach your team
Fits into your CI/CD
Security that doesn't disrupt your workflow
Custom quality gates per application
Automate deployment decisions. Block only what matters
Works in your IDE — VS Code, IntelliJ, Visual Studio
Developers fix issues without ever leaving the editor
What you get

Up to 2x fewer false positives
Your team focuses on real risks, not noise
IDE & CI/CD plugins out of the box
No long setup process
AutoCheck confirms what's exploitable
Automatically, with evidence attached
SAST + SCA + DAST
Plus ML malicious code detection and secrets in code — four risk types, one tool.

23+
years R&D in cyber security
4,000+
enterprise customers worldwide
2,600+
security specialists
31k+
vulnerabilities found in corporate systems annually
An industry leader in results-driven cybersecurity
Positive Technologies is a major global provider of information security products and solutions. Our mission is to safeguard businesses and entire industries against the threat of cyberattacks.
Global vendor covering almost all continents and regions, including SOUTH–EAST ASIA, MENA, LATAM, INDIA, etc.
Client Cases
Faster security testing with fewer false positives

"PT Application Inspector has become an integral part of our ongoing security testing program for dozens of web applications. It filters out false positives and irrelevant results, allowing us to optimize our AST processes and focus on real threats instead of searching for them like a needle in a haystack."
Juergen Streit
Director of Worldwide IT Security
Tech Data
Accelerating secure software delivery
"With 90% of our services delivered digitally, security can’t slow us down. PT Application Inspector ensures accurate vulnerability detection, virtually eliminates false positives, and thanks to incremental scanning — we ship faster without cutting corners on security."
Ilya Zuev
VP of Information Security
A leading digital bank
Clear visibility into real security risks
"This gave our team a clearer view of where the real risks were."
Omar Nuseibeh
Head of Digital Services
Arab Islamic Bank
Enabling DevSecOps without slowing Innovation
"Thanks to the comprehensive SAST & DAST solution provided by Positive Technologies, we have maintained our fast go-to-market pace for new services. We have also established effective collaboration between development and security teams while ensuring strong protection for both existing and new applications."
Dmitry Kostikov
Head of Information Security
A major financial services group
Securing e-banking without slowing delivery
"The standards for e-banking development at our company are exceptionally strict with respect to code quality, vulnerability detection, and remediation speed. We equally care about making sure that all e-banking updates reach our clients on time and do not introduce any new errors. PT Application Inspector proved to be the exact solution we needed — optimizing our AST processes so we never have to compromise between bulletproof security and fast time-to-market."
Director of Information Security
A major commercial bank
Strengthening cyberdefense through real-world simulation
"The city simulation infrastructure was incredibly detailed and realistic, providing a robust environment for our team to engage in the cyberbattle. It added a practical dimension to the competition that was both challenging and educational."
Nur Qurratu Aini Rohizan
Analyst
MyCERT — CyberSecurity Malaysia
Request a demo
We will get back within one business day with a tailored pilot plan.
I give my consent to the processing of my personal data in accordance with the terms of the Privacy Notice.
or write to us directly on info@positech.id (local team available for Indonesia & SEA)
Сообщение об успешной отправке!
FAQ
None of the Gartner leaders offer all these capabilities: proprietary DPI extracting 2,000 session parameters, three independent detection layers with near-zero false positives, and retrospective analysis re-checking traffic history against new threat intelligence when it becomes available.
Yes. PT NAD detects attacker behavior inside TLS through side-channel signatures, reputation indicators on TLS SNI fields, and behavioral patterns.
Yes. PT NAD deploys a virtual sensor in AWS and GCP via native traffic mirroring and runs the same full proprietary DPI engine as on-premises. No additional licenses required for cloud coverage.
No. PT NAD is passive — it only receives a copy of traffic and never sits inline. Zero impact on network performance, no risk of downtime, no agents on endpoints.
PT NAD adds what neither covers: internal network traffic visibility at the application layer. SIEM collects logs — attackers can manipulate them or avoid generating them entirely. EDR watches endpoints — attackers move between them using the network. PT NAD + SIEM + EDR together cover what none of them can cover alone.
No. In an on-premises deployment, all raw traffic and metadata are stored locally. PT NAD does not require cloud connectivity to function, process ML, or access stored data. Nothing is transmitted externally.
Yes. Insider activity creates network anomalies — unusual data transfers, connections to unauthorized destinations, large data volumes at unusual times, use of external proxy servers.
Is my data safe during the pilot?
Yes. You can run the pilot entirely in your own environment (on-prem or private cloud). Your source code stays under your control at all times.
Does Application Inspector slow down your CI/CD pipeline?
Nо. Scans are fast and incremental — only changed code is re-analyzed. You can set quality gates to block only on critical issues, so non-critical findings never delay your build.
What programming languages are supported?
C/C++, C#, Go, Java, JavaScript, TypeScript, Kotlin, Objective-C, Python, PHP, Ruby, Scala, Solidity, Swift, SQL — and hundreds of frameworks built on top of them. Malicious code detection currently covers Python, JavaScript and TypeScript; the rest of the analysis covers the full list above.


Cookies help us improve the user experience on our site. By continuing to use the site, you consent to the use of cookies and the processing of your data. More details can be found via the link